

Easy To Download Microsoft MS-101 Exam Dumps Updated 408 Questions
New Updated MS-101 Exam Questions 2024
Microsoft MS-101 certification exam is designed for IT professionals who are responsible for managing Microsoft 365 services and mobility and security. Microsoft 365 Mobility and Security certification exam is intended for candidates who have experience working with Microsoft 365 technologies and are interested in demonstrating their skills and knowledge in this area. MS-101 exam covers topics such as implementing modern device management, securing data and devices, and managing Microsoft 365 governance and compliance.
Target Audience and Requirements
The intended candidates for the MS-101 exam are the professionals who perform duties associated with planning, evaluating, deploying, migrating, and managing Microsoft 365 services. These individuals are able to execute the Microsoft 365 tenant management tasks for the business needs, including compliance, identities, security, and assistive technologies.
Before registering for the Microsoft MS-101 test, the students need to make sure that they possess the requisite knowledge and skills. They should be conversant with Microsoft 365 workloads and hold the role of an Administrator in one of the following workloads: Skype for Business, Exchange, Windows as a Service, and/or SharePoint. A good grasp of server administration, networking, and IT basics, such as DNS, Active Directory, and PowerShell, will be an added advantage.
Microsoft MS-101: Microsoft 365 Mobility and Security is a certification exam designed for IT professionals who want to demonstrate their expertise in Microsoft's cloud-based technologies. MS-101 exam focuses on Microsoft 365, which is a suite of productivity tools that includes Office 365, Windows 10, and Enterprise Mobility and Security.
NEW QUESTION # 169
You have a Microsoft 365 tenant.
You discover that administrative tasks are unavailable in the Microsoft Office 365 audit logs of the tenant.
You run the Get-AdminAuditLogConfig cmdlet and receive the following output:
You need to ensure that administrative tasks are logged in the Office 365 audit logs.
Which attribute should you modify?
- A. AdminAuditLogEnabled
- B. TestCmdletLoggingEnabled
- C. UnifiedAuditLogIngestionEnabled
Answer: C
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/powershell/module/exchange/policy-and-compliance-audit/set-adminauditlogco
NEW QUESTION # 170
You have a Microsoft Azure Active Directory (Azure AD) tenant named contoso.com.
A user named User1 has files on a Windows 10 device as shown in the following table.
In Azure Information Protection, you create a label named Label1 that is configured to apply automatically.
Label1 is configured as shown in the following exhibit.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
The phrase to match is "im" and it is case sensitive. The phrase must also appear at least twice.
Box 1: No
File1.docx contain the word "import" once only
Box 2: Yes
File2.docx contains two occurrences of the word "import" as well as the word "imported" Box 3: No File3.docx contains "IM" but his is not the correct letter case.
References:
https://docs.microsoft.com/en-us/azure/information-protection/configure-policy-classification
NEW QUESTION # 171
You purchase a new Microsoft 365 subscription.
You create 100 users who are assigned Microsoft 365 E3 licenses.
From the Security & Compliance admin center, you enable auditing.
Six months later, a manager sends you an email message asking the following questions:
* Question1: Who created a team named Team1 14 days ago?
* Question2: Who signed in to the mailbox of User1 30 days ago?
* Question3: Who changed the site collection administrators of a site 60 days ago?
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation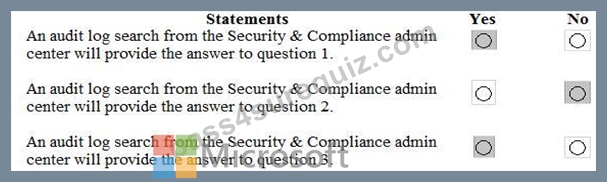
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/search-the-audit-log-in-security-and-compliance?
https://docs.microsoft.com/en-us/office365/securitycompliance/enable-mailbox-auditing
NEW QUESTION # 172
Your company uses Microsoft Cloud App Security.
You plan to integrate Cloud App Security and security information and event management (SIEM).
You need to deploy a SIEM agent on a server that runs Windows Server 2016.
What should you do? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/integrate-your-siem-server-with-office-365-cas
NEW QUESTION # 173
You have a Microsoft 365 E5 subscription that contains the devices shown in the following table.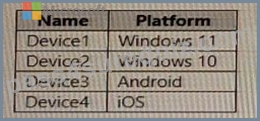
All the devices are onboarded To Microsoft Defender for Endpoint
You plan to use Microsoft Defender Vulnerability Management to meet the following requirements:
* Detect operating system vulnerabilities.
Answer:
Explanation:
Explanation
NEW QUESTION # 174
Your company purchases a cloud app named App1.
You need to ensure that you can use Microsoft Cloud App Security to block downloads in App1. App1 supports session controls.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation
Graphical user interface, text, application Description automatically generated
Reference:
https://docs.microsoft.com/en-us/cloud-app-security/getting-started-with-cloud-app-security
NEW QUESTION # 175
You configure a conditional access policy. The locations settings are configured as shown in the Locations exhibit. (Click the Locations tab.)
The users and groups settings are configured as shown in the Users and Groups exhibit. (Click Users and Groups tab.)
Members of the Security reader group report that they cannot sign in to Microsoft Active Directory (Azure AD) on their device while they are in the office.
You need to ensure that the members of the Security reader group can sign in in to Azure AD on their device while they are in the office. The solution must use the principle of least privilege.
What should you do?
- A. From the Endpoint Manager admin center, create a device compliance policy.
- B. From the conditional access policy, configure the device state.
- C. From the Azure Active Directory admin center, create a custom control.
- D. From the Azure Active Directory admin center, create a named location.
Answer: D
Explanation:
Section: [none]
Explanation/Reference:
https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/location-condition
NEW QUESTION # 176
You have a Microsoft 365 tenant.
You plan to create a retention policy as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 177
You have a Microsoft 365 subscription that contains the users shown in the following table.
You run the following cmdlet.
Set-MailboxAuditBypassAssociation -Identity User2
-AuditByPassEnabled $true
The users perform the following actions:
* User1 accesses an item in the mailbox of User2.
* User2 modifies a mailbox item in the mailbox of User3.
* User3 signs in to her mailbox.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Reference:
https://docs.microsoft.com/en-us/powershell/module/exchange/set-mailboxauditbypassassociation?view=exchan
NEW QUESTION # 178
You have a Microsoft 365 E5 tenant that contains 500 Android devices enrolled in Microsoft Intune.
You need to use Microsoft Endpoint Manager to deploy a managed Google Play app to the devices.
Which four actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation
Graphical user interface, text, application Description automatically generated
Reference:
https://docs.microsoft.com/en-us/mem/intune/apps/apps-add-android-for-work#assign-a-managed-google-play-a
NEW QUESTION # 179
You need to recommend a solution for the security administrator. The solution must meet the technical requirements.
What should you include in the recommendation?
- A. Microsoft Azure Active Directory (Azure AD) authentication methods
- B. Microsoft Azure Active Directory (Azure AD) conditional access policies
- C. Microsoft Azure Active Directory (Azure AD) Privileged Identity Management
- D. Microsoft Azure Active Directory (Azure AD) Identity Protection
Answer: B
Explanation:
Explanation/Reference:
References:
https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/untrusted-networks Question Set 1
NEW QUESTION # 180
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an Active Directory domain named contoso.com that is synced to Microsoft Azure Active Directory (Azure AD).
You manage Windows 10 devices by using Microsoft System Center Configuration Manager (Current Branch).
You configure pilot co-management.
You add a new device named Device1 to the domain. You install the Configuration Manager client on Device1.
You need to ensure that you can manage Device1 by using Microsoft Intune and Configuration Manager.
Solution: You add Device1 to an Active Directory group.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
Explanation:
References:
https://www.scconfigmgr.com/2017/11/30/how-to-setup-co-management-part-6/
Topic 1, Contoso, Ltd
Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and two branch offices in Seattle and New York.
The company has the employees and devices shown in the following table.
Contoso recently purchased a Microsoft 365 ES subscription.
Existing Environment
Requirement
The network contains an on-premises Active Directory forest named contoso.com. The forest contains the servers shown in the following table.
All servers run Windows Server 2016. All desktops and laptops are Windows 10 Enterprise and are joined to the domain.
The mobile devices of the users in the Montreal and Seattle offices run Android. The mobile devices of the users in the New York office run iOS.
The domain is synced to Azure Active Directory (Azure AD) and includes the users shown in the following table.
The domain also includes a group named Group1.
Planned Changes
Contoso plans to implement the following changes:
* Implement Microsoft 365.
* Manage devices by using Microsoft Intune.
* Implement Azure Advanced Threat Protection (ATP).
* Every September, apply the latest feature updates to all Windows computers. Every March, apply the latest feature updates to the computers in the New York office only.
Technical Requirements
Contoso identifies the following technical requirements:
* When a Windows 10 device is joined to Azure AD, the device must enroll in Intune automaticaiy.
* Dedicated support technicians must enroll all the Montreal office mobile devices in Intune.
* User1 must be able to enroll all the New York office mobile devices in Intune.
* Azure ATP sensors must be installed and must NOT use port mirroring.
* Whenever possible, the principle of least privilege must be used.
* A Microsoft Store for Business must be created.
Compliance Requirements
Contoso identifies the following compliance requirements:
* Ensure that the users in Group1 can only access Microsoft Exchange Online from devices that are enrolled in Intune and configured in accordance with the corporate policy.
* Configure Windows Information Protection (W1P) for the Windows 10 devices.
NEW QUESTION # 181
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a Microsoft 365 subscription.
From the Security & Compliance admin center, you create a role group named US eDiscovery Managers by copying the eDiscovery Manager role group.
You need to ensure that the users in the new role group can only perform content searches of mailbox content for users in the United States.
Solution: From Windows PowerShell, you run the New-ComplianceSecurityFiltercmdlet with the appropriate parameters.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
Explanation:
Section: [none]
Explanation/Reference:
References:
https://docs.microsoft.com/en-us/office365/securitycompliance/permissions-filtering-for-content-search
https://docs.microsoft.com/en-us/powershell/module/exchange/policy-and-compliance-content-search/new- compliancesecurityfilter?view=exchange-ps
NEW QUESTION # 182
You have a Microsoft 365 E5 subscription that uses Microsoft Defender for Cloud Apps.
You need to be notified when a single user downloads more than 50 files during any 60-second period.
What should you configure?
- A. an anomaly detection policy
- B. a file policy
- C. a session policy
- D. an activity policy
Answer: A
NEW QUESTION # 183
You have a Microsoft 365 tenant.
You plan to create a retention policy as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.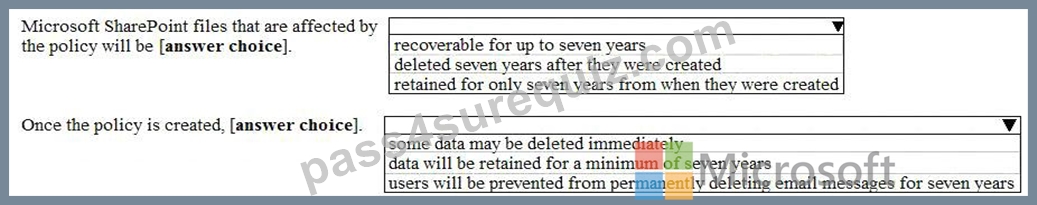
Answer:
Explanation:
Explanation
NEW QUESTION # 184
Your company has a Microsoft 365 E3 subscription.
All devices run Windows 10 Pro and are joined to Microsoft Azure Active Directory (Azure AD).
You need to change the edition of Windows 10 to Enterprise the next time users sign in to their computer. The solution must minimize downtime for the users.
What should you use?
- A. an in-place upgrade
- B. Subscription Activation
- C. Windows Autopilot
- D. Windows Update
Answer: D
NEW QUESTION # 185
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have a computer that runs Windows 10.
You need to verify which version of Windows 10 is installed.
Solution: From the Settings app, you select to view the update history.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
NEW QUESTION # 186
You have Microsoft 365 subscription.
You create an alert policy as shown in the following exhibit.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Note: The Aggregation settings has a 120 minute window
NEW QUESTION # 187
You have a Microsoft 365 E5 subscription.
Several users have iOS devices.
You plan to enroll the iOS devices in Microsoft Endpoint Manager.
You need to ensure that you can create an iOS/iPadOS enrollment profile in Microsoft Endpoint Manager.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
1 - From the Microsoft Endpoint Manager admin center,download a certificate signing request.
2 - Create a certificate from the Apple Push Certificates Portal.
3 - Upload an Apple MDN push certificate to Microsoft Endpoint Manager.
Reference:
https://docs.microsoft.com/en-us/mem/intune/enrollment/apple-mdm-push-certificate-get
NEW QUESTION # 188
Your company uses Microsoft Defender Advanced Threat Protection (Microsoft Defender ATP).
The devices onboarded to Microsoft Defender ATP are shown in the following table.
The alerts visible in the Microsoft Defender ATP alerts queue are shown in the following table.
You create a suppression rule that has the following settings:
Triggering IOC: Any IOC
Action: Hide alert
Suppression scope: Alerts on ATP1 machine group
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 189
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an on-premises Active Directory domain. The domain contains 2,000 computers that run Windows 8.1 and have applications installed as shown in the following table.
You enroll all the computers in Upgrade Readiness.
You need to ensure that App1 and App2 have an UpgradeDecision status of Ready to upgrade.
Solution: You set the importance status of App2 to Low install count.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
Explanation:
Explanation
If an app is installed on less than 2% of the targeted devices, it's marked Low install count. Two percent is the default value. You can adjust the threshold in the readiness settings from 0% to 10%. Desktop Analytics automatically marks these apps as Ready to upgrade.
Reference:
https://docs.microsoft.com/en-us/configmgr/desktop-analytics/about-deployment-plans
NEW QUESTION # 190
Your company uses Microsoft Cloud App Security.
You plan to integrate Cloud App Security and security information and event management (SIEM).
You need to deploy a SIEM agent on a server that runs Windows Server 2016.
What should you do? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
https://docs.microsoft.com/en-us/office365/securitycompliance/integrate-your-siem-server-with-office-365-cas
NEW QUESTION # 191
HOTSPOT
You have a Microsoft 365 subscription.
You create a Microsoft Cloud App Security policy named Risk1 based on the Logon from a risky IP address template as shown in the following exhibit.
You have two users named User1 and User2. Each user signs in to Microsoft SharePoint Online from a risky IP address 10 times within 24 hours.
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
Hot Area:
Answer:
Explanation:
Section: [none]
NEW QUESTION # 192
......
Updated Free Microsoft MS-101 Test Engine Questions with 408 Q&As: https://www.pass4surequiz.com/MS-101-exam-quiz.html
The Best Microsoft 365 MS-101 Professional Exam Questions: https://drive.google.com/open?id=1VCutAf2wrCgoArIOrZ7s-g45qDWGjRvW